Governance OS for healthcare compliance · Senior care to health systemsA ReMyll product ↗
Platform

The platform.

Seven governance modules writing to one governance record, so evidence assembled for one survey is already in place for the next. Open any module for its capabilities and what it produces when a regulator or auditor asks.

Book a demo →Talk to us
Core governance modules

One operating system. Every compliance program.

Each module writes to the same ledger.

Evidence assembled for one survey is already in place for the next. Policies, incidents, credentials, and vendors carry the same owner, status, and time stamp, so the program reads as one account rather than seven systems.

Abastyan Governance OS
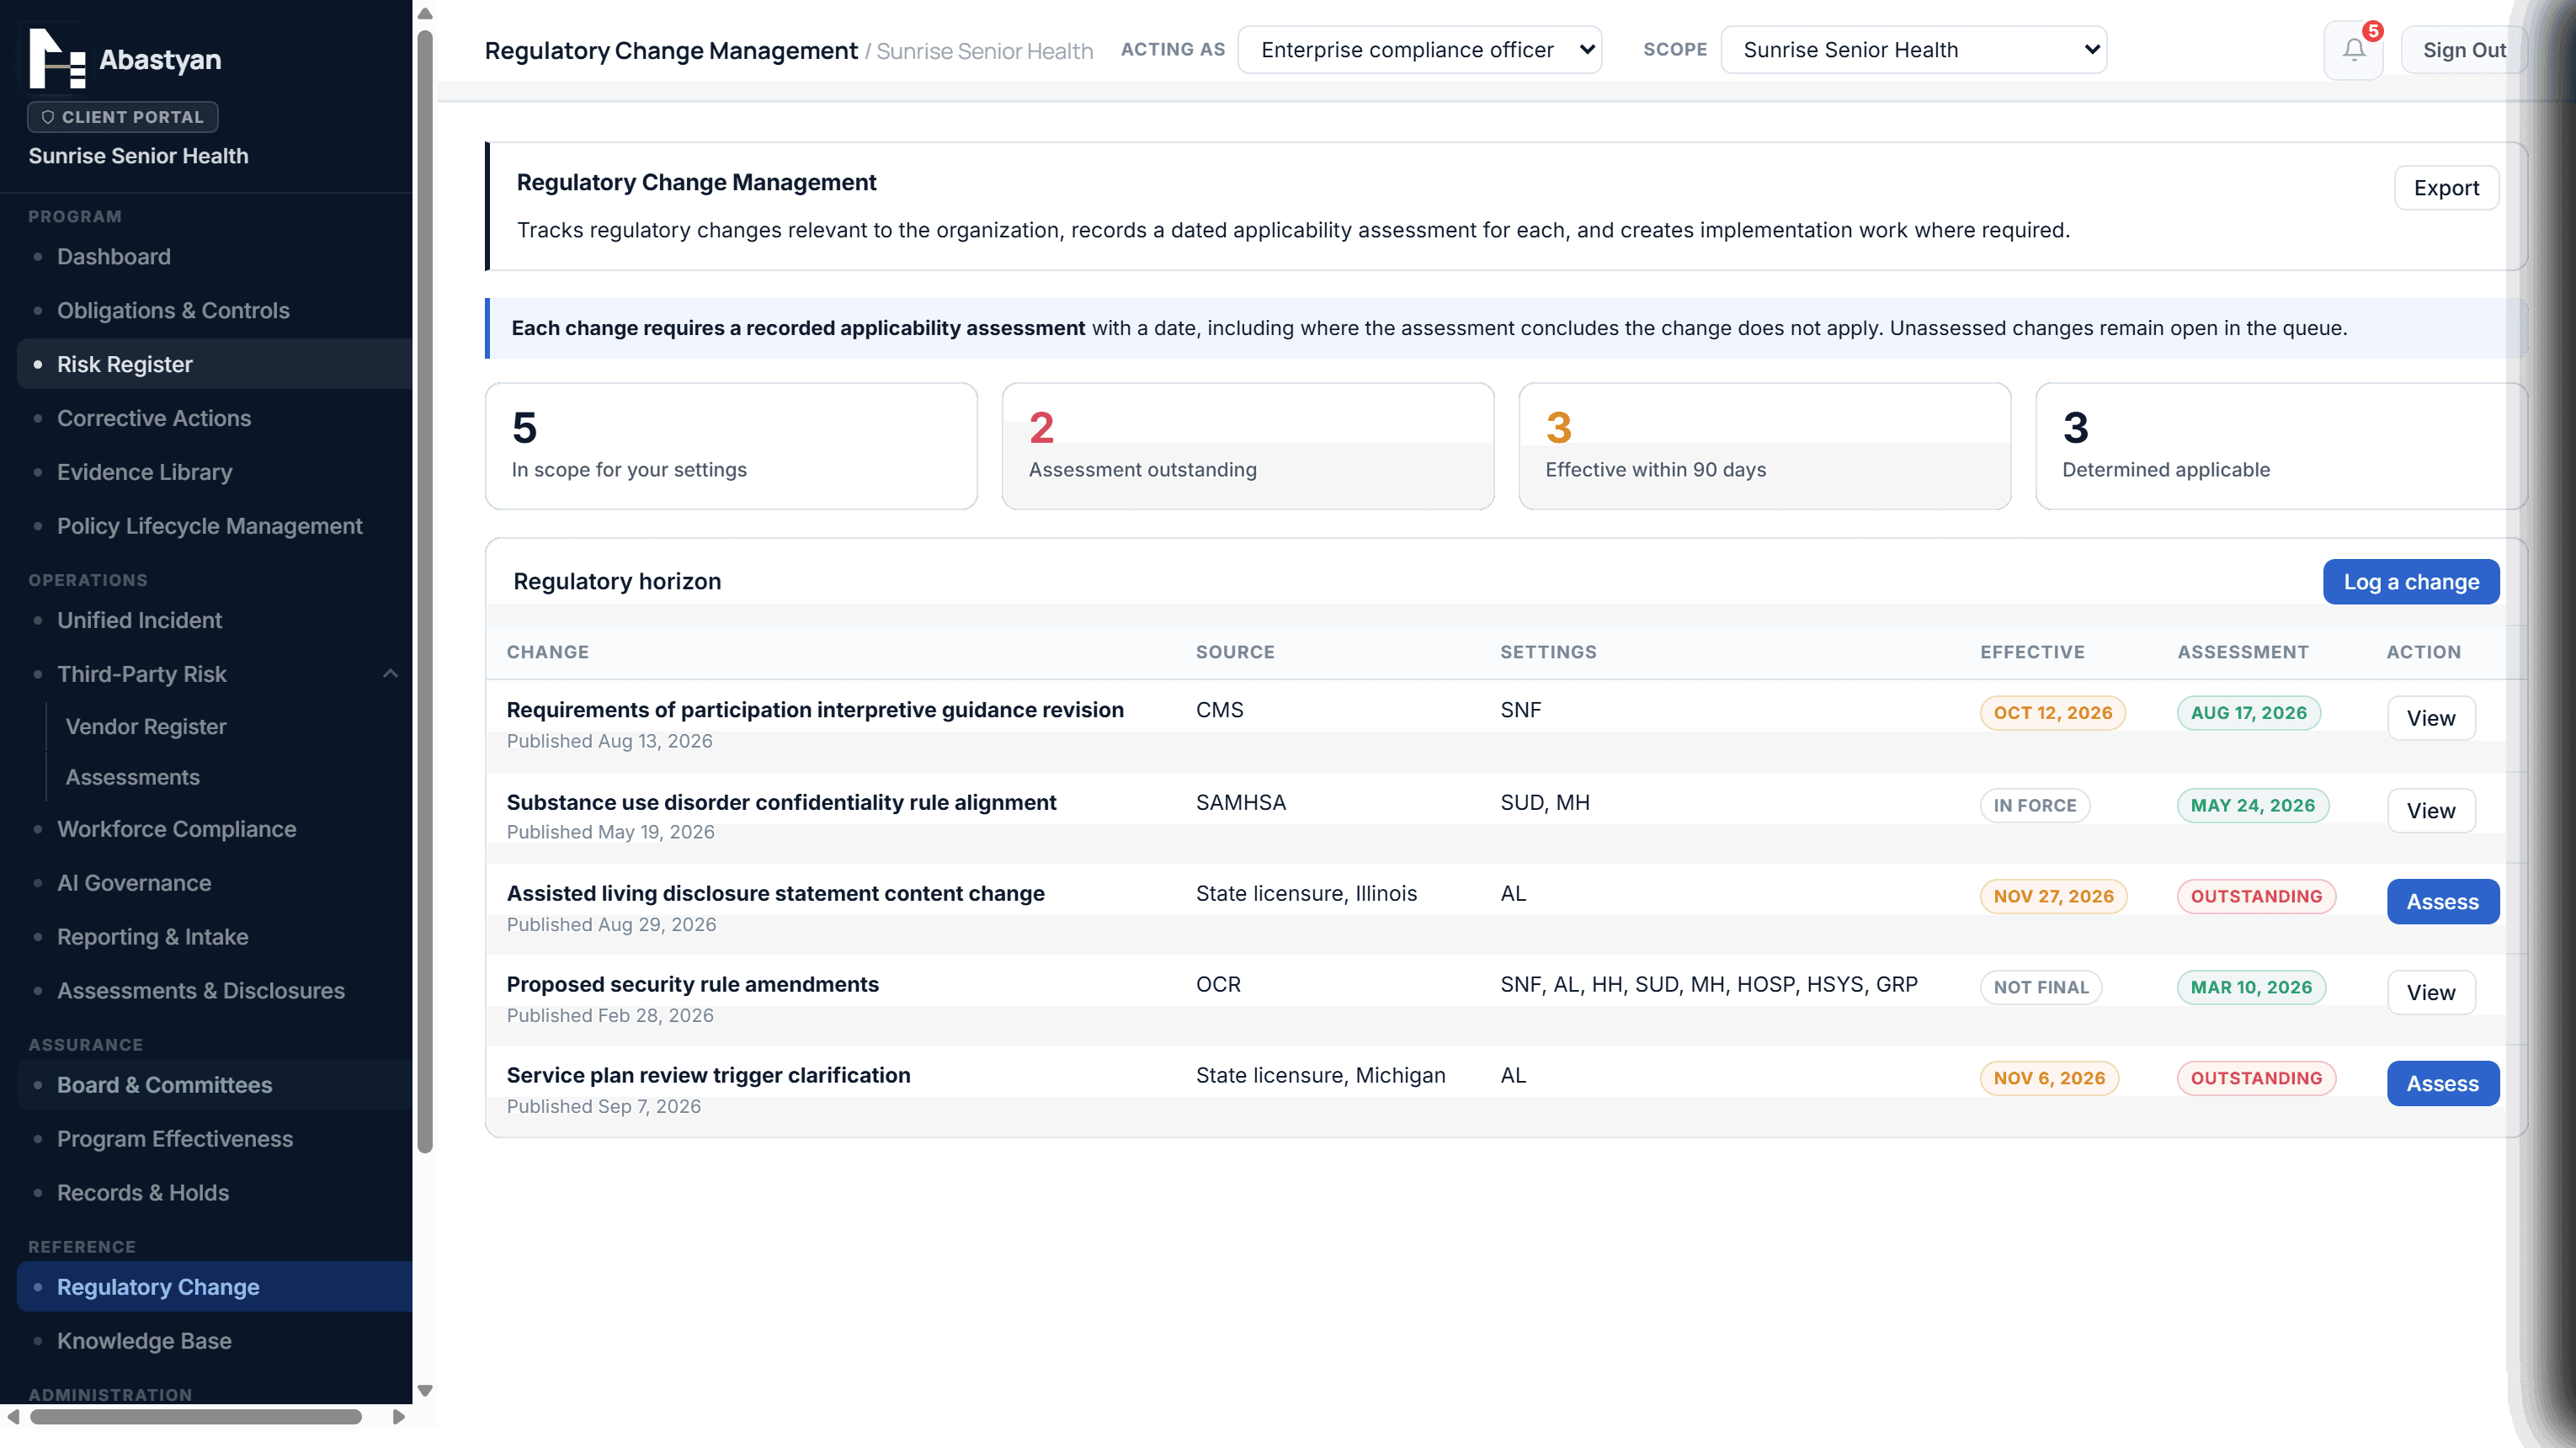
Abastyan regulatory alerts with owners, deadlines, and the module rail
Alerts with an owner
Federal and state changes routed to an owner with a due date
Deadlines ahead of time
Survey windows and effective dates on one timeline
Every facility in view
Program health across the whole footprint
What Abastyan brings togetherSeven modules, one record. Select a module to see what it holds.
Module 01 of 07

Audit Readiness & Assessments

Evidence ready before anyone asks.

Internal reviews and external evidence in a secure central hub, crosswalked to the requirement each reviewer will cite.

Key capabilities
Regulatory crosswalk
Internal assessments
Evidence hub
Readiness score
Open the module page →
Why Abastyan

The cost of fragmented governance is measurable.

Healthcare organizations spend significant internal time reconciling compliance work across disconnected tools. Abastyan brings that work into one system, so leaders see the program clearly and teams spend less time assembling and reconciling records.

When every policy has an owner and a version, every incident a root cause and a corrective action, and every credential and agreement an accountable expiry, the evidence a surveyor, auditor, or investigator asks for already exists in the record.

Operational and financial exposurePublished sources
HIPAA civil monetary penalties
Tiered by culpability; annual caps per violation category adjusted for inflation.
HIPAA
CMS civil money penalties for nursing facilities
Per-day and per-instance penalties for noncompliance with participation requirements.
CMS
Denial of payment for new admissions
A remedy imposed when deficiencies remain uncorrected past the survey cycle.
CMS
OIG exclusion and CMP exposure
Employing or contracting with excluded individuals carries per-item civil penalties.
OIG
Figures reflect publicly reported ranges and vary by jurisdiction, facility type, and circumstance. Abastyan supports, but does not guarantee, any regulatory outcome.
Connected products

Each stands on its own. Together they write to one record.

Separate ReMyll products, sold and priced independently. When connected, each sends Abastyan only what the governance record needs. Everything else stays where it is.

ABASTYAN6 modules fed
Reporting and intake viewfrom ARIA
Program dashboardfrom ARIA
Reporting line exportfrom ARIA
AI governance inventoryfrom AITPRM
Bias impact assessmentsfrom AITPRM
Third-party riskfrom AITPRM

Select a product to highlight what it feeds.

Compliance hotline

ARIA Hotline

AI intake on a 24/7 voice line and branded web channel, delivering a structured case file for human review.

On its own
  • Structured, policy-aligned interview
  • Time-stamped, categorized case file
  • Anonymous reporting with two-way follow-up
Sends to Abastyan
Report volume, timing, and substantiation by category and site
Stays in ARIA
Reports, case files, and reporter identity
AI vendor risk management

AITPRM Health

Evaluates AI vendors across twelve healthcare-specific risk domains, with sample contract language for each finding.

On its own
  • Twelve scored AI risk domains
  • Assessment matched to the vendor’s scope
  • Sample contract language for each finding
Sends to Abastyan
Your vendor list, with AI vendors flagged for governance review
Stays in AITPRM
Questionnaire responses, scores, and findings